
You’re accessing archived content
This is archived content from the UIT website. Information may be outdated, and links may no longer function. Please contact stratcomm@it.utah.edu if you have any questions about archived content.
How to recognize phishing
Select the image for a larger version.
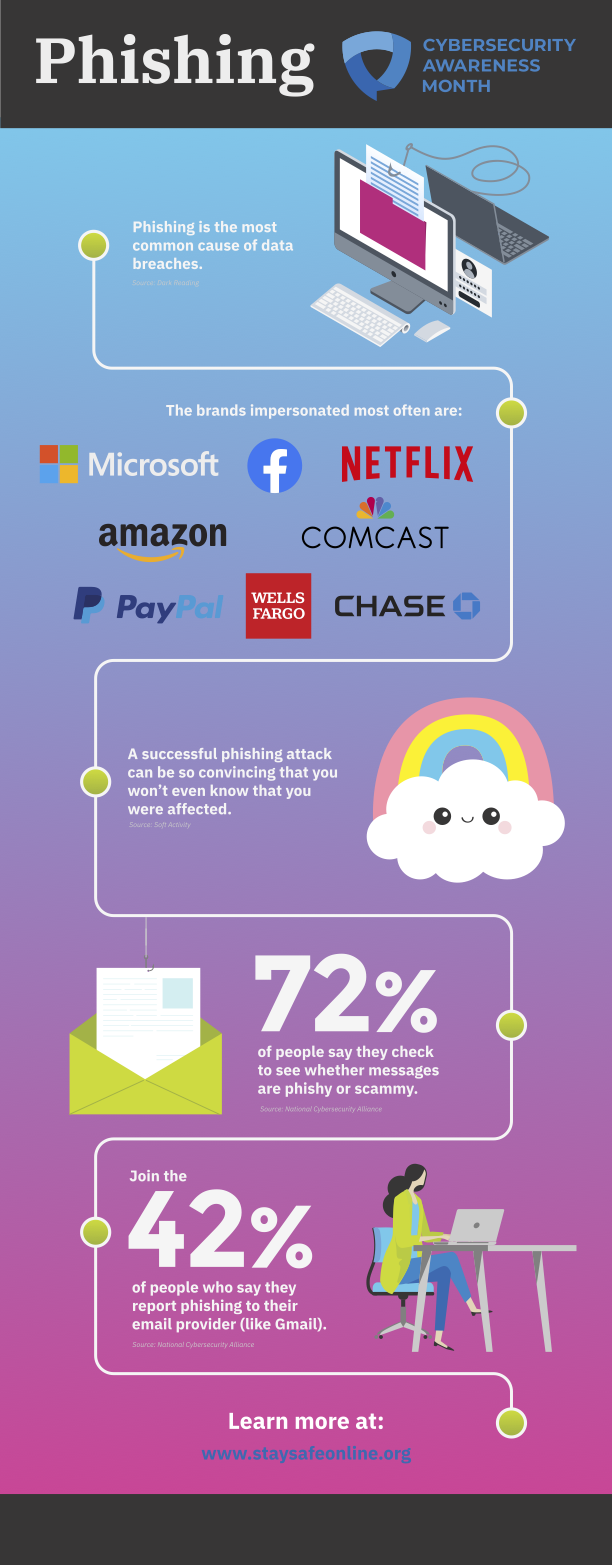
An infographic on phishing, with the Cybersecurity Awareness Month logo in the top right and a blue to pink gradient for a background. A line flows from top to bottom with green dots marking important facts.
Fact 1: Text that reads, "Phishing is the most common cause of data breaches." to the left of a graphic of a desktop computer and laptop show the laptop using a line with a hook to phish a document contained in a pink folder on the desktop. The phisher wants credentials, shown to the right.
Fact 2: Text that reads, "The brands impersonated most often are:" with the Microsoft, Facebook, Netflix, Amazon, Comcast, PayPal, Wells Fargo, and Chase logos below the text.
Fact 3: Text that reads, "A successful phishing attack can be so convincing that you won't even know that you were affected." to the left of an illustration of a pink, yellow, and blue rainbow that sits on top of a white cloud with googly eyes and rosy cheeks.
Fact 4: Text that reads, "72% of people say they check to see whether messages are phishing or scammy." to the right of an illustration of a green email icon with an open document that's hanging on a fishing hook.
Fact 5: Text that reads, "Join the 42% of people who say they report phishing to their email provider (like Gmail)." to the left of an illustration of a woman sitting at a desk and using a laptop computer. The woman wears an open, green sweater, blue shirt, and blue pants. She sits on a blue office chair.
Learn more at: wwww.staysafeonline.org
Phishing is a scam designed to steal information or passwords, compromise devices, or trick you out of money. While we often think of phishing as being limited to emails, it can also take the form of deceptive text messages (smishing), posts on social media, pop-ups, or phone calls (vishing).
Phishers may ask for your name, account information, date of birth, Social Security number, address, etc. They may also try to get you to open a link or file. Hover or tab over any links to review exactly where you are being directed. If it's not legit, don't open it.
Types of phishing and phishing 'hooks'
Phishing is a way criminals use social engineering to trick you into sharing private and confidential data, such as bank account numbers or login information. Criminals employ many methods, such as:
- Phishing
- Generic, everyday phishing is not targeted and tends to be easier to spot.
- Spear phishing
- Spear phishing is one of the most dangerous forms of phishing. The phisher targets a specific individual and studies them to be able to write a more convincing, legitimate-looking message to trick them into letting down their guard and sharing sensitive information.
- Whaling
- Also known as CEO fraud, whaling specifically targets chief executive officers and senior leadership.
- Shared document phishing
- You might receive an email that appears to come from file-sharing sites like UBox, Dropbox, Google Drive, or OneDrive alerting you that a document has been shared with you. The link provided in these emails will take you to a fake login page that mimics a real login page and will steal your account credentials.
Indicators that an email isn’t legitimate:
- The sender isn’t specified, isn’t someone you know, or doesn’t match the “from” address
- Unfamiliar, unusual, or generic greetings; it’s not addressed to you, specifically,
by name
- [No greeting]
- Dear member
- Hello friend
- Spelling and grammar errors
- Suspicious links
- A link that doesn’t match the URL of the webpage stated in the email
- A link to pictures or videos from people you don’t know
- A link or attachment to view an unexpected e-card or to track an unknown package
- Attachments
- Incorrect or suspicious filenames
- Suspicious file extensions (e.g., .bin, .com, .exe, .html, .pif, .vbs, .zip, .zzx)
- Low-resolution images
Reputable organizations like the University of Utah will never email you for your password, Social Security number, or any confidential or personal information. Visit our Phish Tank to learn more about various phishing schemes and how to avoid them.
How to report phishing
Resource
Watch our Beware of Phishing scams video to learn more.
If you receive a phishing email in your UMail account, immediately report it using the Phishing Alert Button — the simplest and the fastest way to report suspicious messages to the Information Security Office (ISO).
If your email client does not have the Phish Alert Button, forward the email as an attachment to phish@utah.edu. If you are unsure how to forward a message as an attachment, use a search engine (e.g., Google) to find instructions for your email client.
Once you report the email, the ISO’s Security Operations Center (SOC) will review the suspicious email, notify users whether it is malicious, and act as needed to protect users and the university.
If, by accident, you open a questionable link and enter your university credentials, immediately go to the CIS website — https://cis.utah.edu/ — and change your password. In addition, contact the SOC at soc@utah.edu to notify information security staff.